
Criminals Are Now Using LLMs to Triage Stolen Credentials at Scale
A free, open-source tool circulating on the exploit.in cybercrime forum is using a commercial large language model to automate what used to be the most labor-intensive part of monetizing infostealer logs: figuring out what's actually inside each compromised account.
The tool, called AUTOMATIC MACHINE, was released as source code in August by a forum member who claims to have earned over $100,000 processing public stealer logs with it. It ingests raw log archives (ZIP or RAR, including password-protected ones), extracts url:login:password combinations, checks which sites are alive, and then uses a stealth browser to log into accounts, solve CAPTCHAs, and crawl the authenticated session.
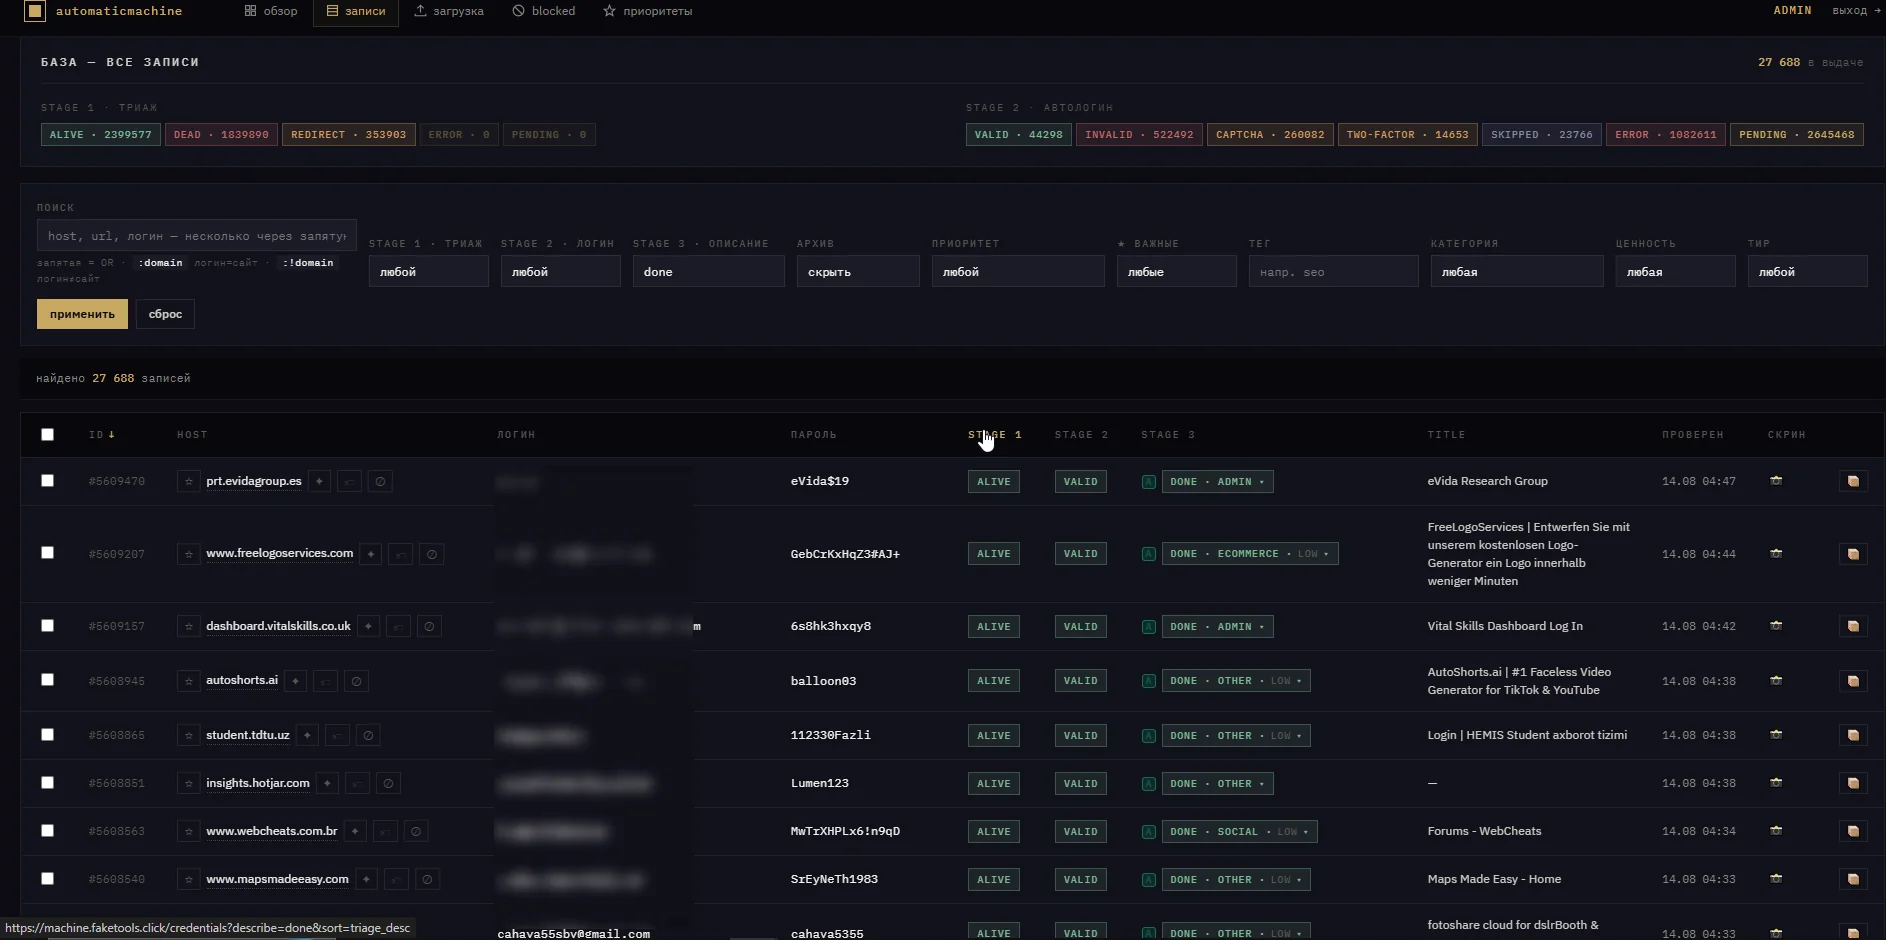
The final stage is where the economics shift. The tool feeds the crawled account data to DeepSeek's API, which reads it like a live auditor and returns structured JSON: login status, service category, visible balances, account restrictions, and a plain-language description of the account's contents. Results are sorted into value tiers (S through D) across categories like banking, crypto, advertising dashboards, and hosting. The descriptions become full-text searchable, turning a pile of logs into a queryable inventory of monetizable accounts.
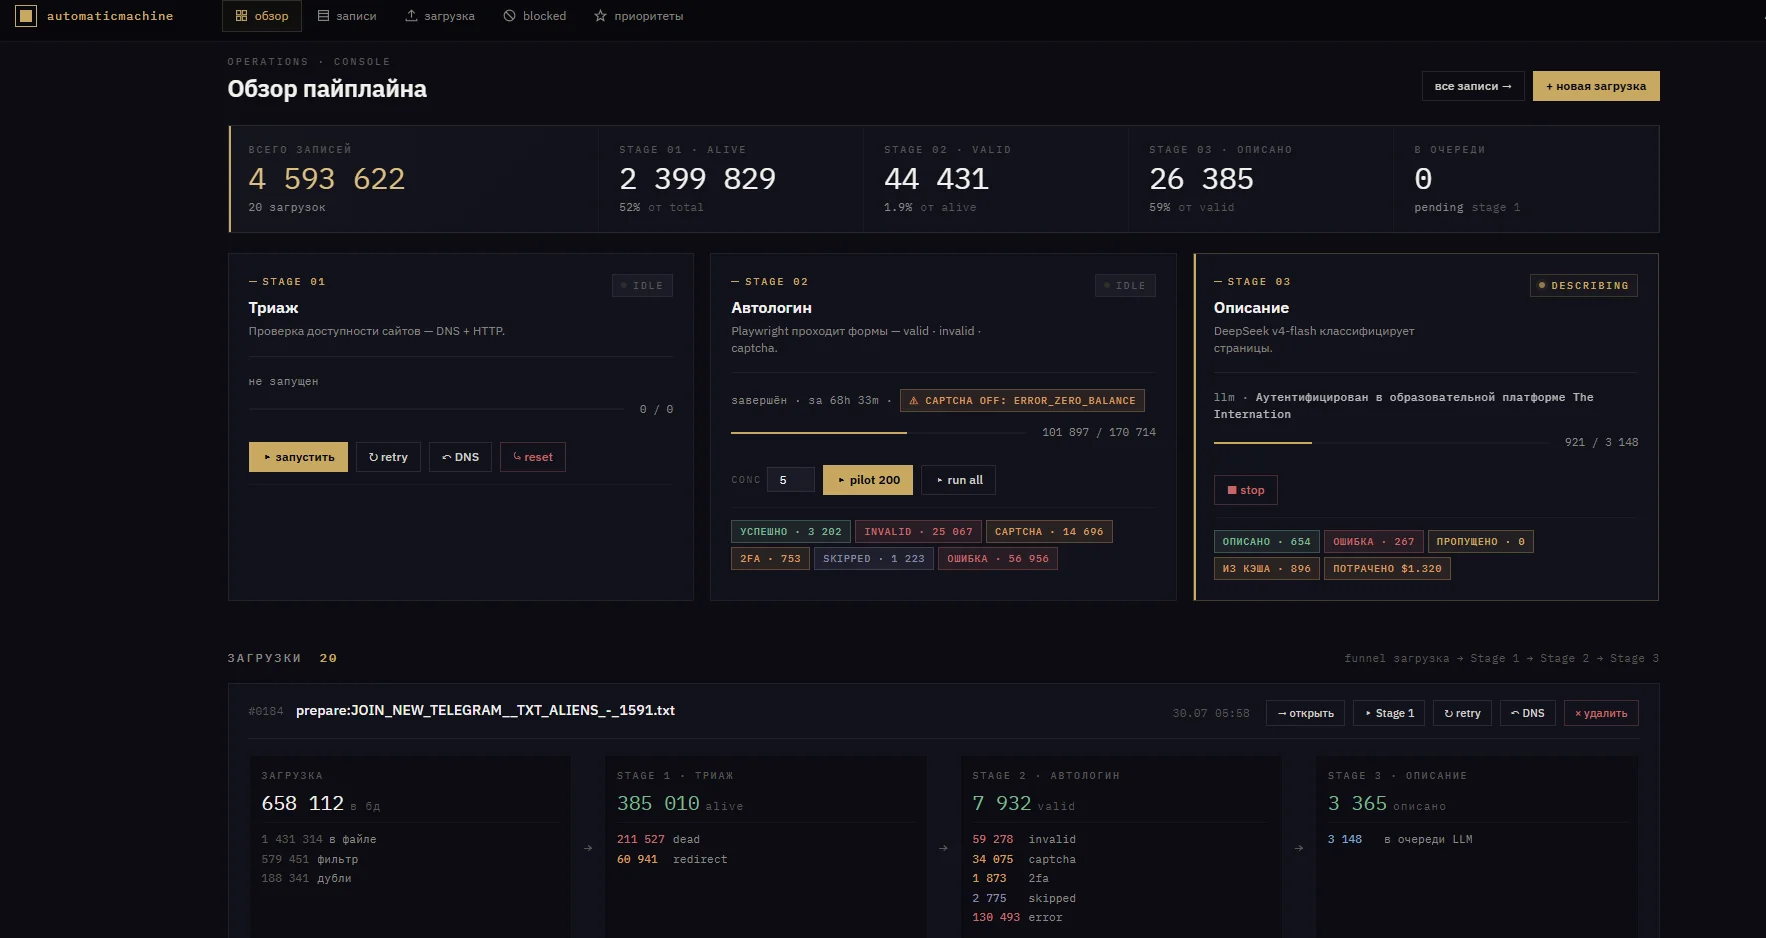
"The alternative without an LLM is a person opening every account with their own eyes," the author wrote. "On hundreds of thousands of records, that's physically impossible."
Community development is ongoing. Recent additions include CAPTCHA-solver API support, rotating proxy pools, and a proposal, already under discussion, to have the LLM audit its own findings and generate new search keywords for future scans, creating a self-improving discovery loop. Users are also asking about porting the pipeline to local models like Qwen to eliminate third-party API costs and reduce exposure.
The release marks a commoditization step for credential abuse: account appraisal, once skilled manual labor, is now free tooling whose only marginal cost is API tokens. For defenders, it means the lag between credential theft and exploitation will keep shrinking, and that stolen-credential monitoring and rapid invalidation matter more than ever.
The lag between credential theft and exploitation keeps shrinking. At HackedList.io, we track it as it happens.
We monitor live stealer logs, darknet marketplaces, and criminal forums, so you find out about compromised credentials before they get appraised, tiered and sold.
Want to know if credentials from your organization are already circulating in stealer logs? Enter your domain below to find out: